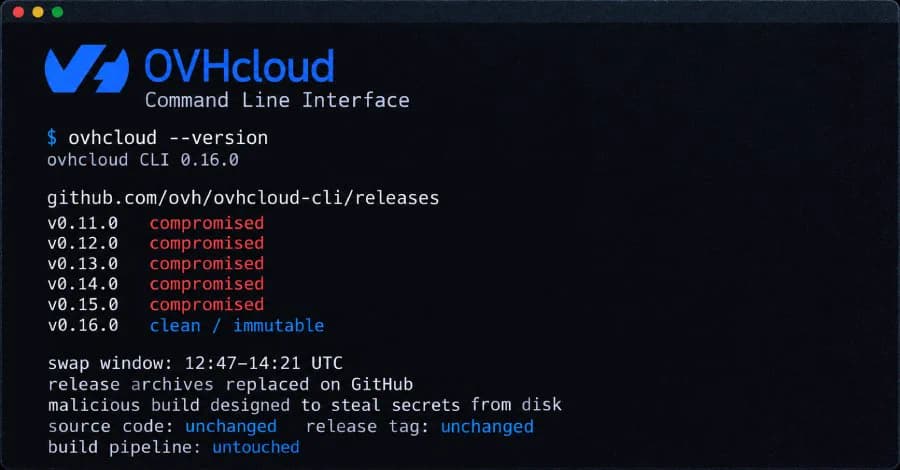
French cloud and hosting provider OVHcloud has warned users that its open-source command-line interface tool was tampered with on Monday, October 19, when attackers replaced legitimate download archives with builds designed to steal sensitive data from affected machines.
How the Attack Unfolded
According to The Hacker News, an attacker gained access to a contributor's GitHub account and used it to swap the download archives on five existing releases of the CLI tool. The replacement files were crafted to harvest secrets stored on the disk of any machine that executed them.
The malicious archives were live on GitHub from 12:47 to 14:21 UTC, a window of up to 94 minutes, before being taken down. OVHcloud subsequently issued a public warning urging users to verify whether they had downloaded any of the affected releases during that period.
What Was Targeted
The malware was described as an information stealer aimed at secrets held on disk, which in a developer context typically means credentials, API keys, tokens, and similar sensitive configuration data. Developers who downloaded and ran the CLI during the exposure window may be at risk.
Scope and Response
OVHcloud confirmed that the compromised account belonged to a contributor rather than a core maintainer, and that the attack vector was account hijacking rather than a vulnerability in the codebase itself. The provider has advised users to treat any secrets accessible on machines that ran the backdoored builds as potentially compromised and to rotate credentials accordingly.
The incident is consistent with a broader pattern of supply-chain attacks targeting open-source tooling distributed through code-hosting platforms, where replacing pre-built release archives can be an effective way to reach a large number of developers without modifying the underlying source code.