OpenCode, an open-source AI coding project, has disclosed a security incident in which an unauthorized party accessed a legacy system and may have exposed API keys that users had stored for third-party AI providers.
What Was Affected
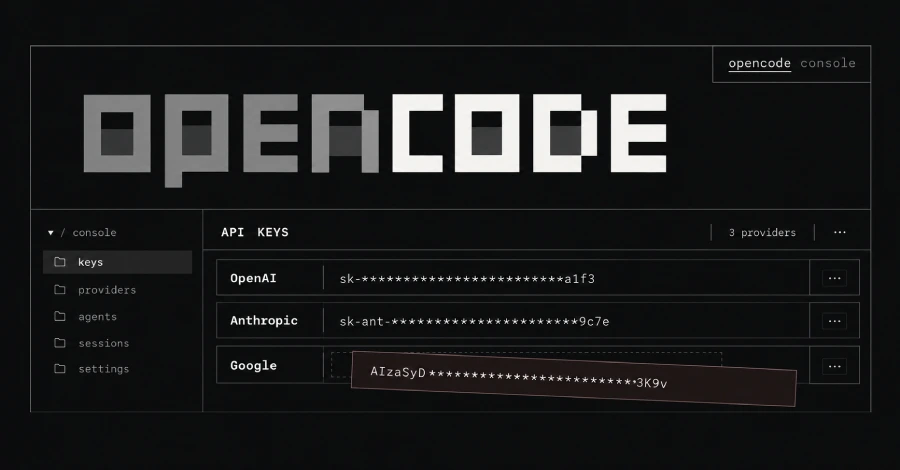
According to The Hacker News, the intrusion occurred on the night of October 16 and targeted a legacy system connected to OpenCode Console, the project's optional hosted service. Console allows teams to store their own API keys for providers such as OpenAI, Anthropic, and Google, enabling team members to share access to those AI models through a single workspace configuration.
BleepingComputer reports that the company has already notified a small number of users whose credentials may have been involved. The scope of the breach appears limited to those who had opted into the Console service and saved provider keys there.
How Console Works
The Console service is distinct from the core OpenCode tool. When a workspace saves an API key in Console, the service uses that key to make calls to the relevant AI provider on behalf of team members. This architecture means that a compromise of Console's storage could expose credentials belonging to multiple external platforms at once.
What Users Should Do
Although neither source specifies the exact remediation steps OpenCode has recommended, users who stored OpenAI, Anthropic, or Google API keys in Console should consider rotating those keys immediately as a precaution. Revoking and reissuing API keys is a standard response to potential credential exposure and prevents an attacker from making unauthorized calls at the key owner's expense.
Context
The incident highlights a recurring risk in developer tooling that aggregates credentials for convenience. Hosted services that centralize API keys can become high-value targets, since a single breach may yield credentials spanning several upstream providers simultaneously.
OpenCode has not publicly detailed how the intruder gained access to the legacy system or whether any keys were actively misused before the breach was discovered.